Incident Response
Lead high-sensitivity investigations, coordinate escalation, and own the response lifecycle through closure.
- Triage
- Containment
- Root cause
- Post-incident reporting
I investigate complex threats, strengthen enterprise defenses, and turn security signals into decisive action. My work spans federal and private-sector environments, grounded in more than a decade of hands-on cyber defense.
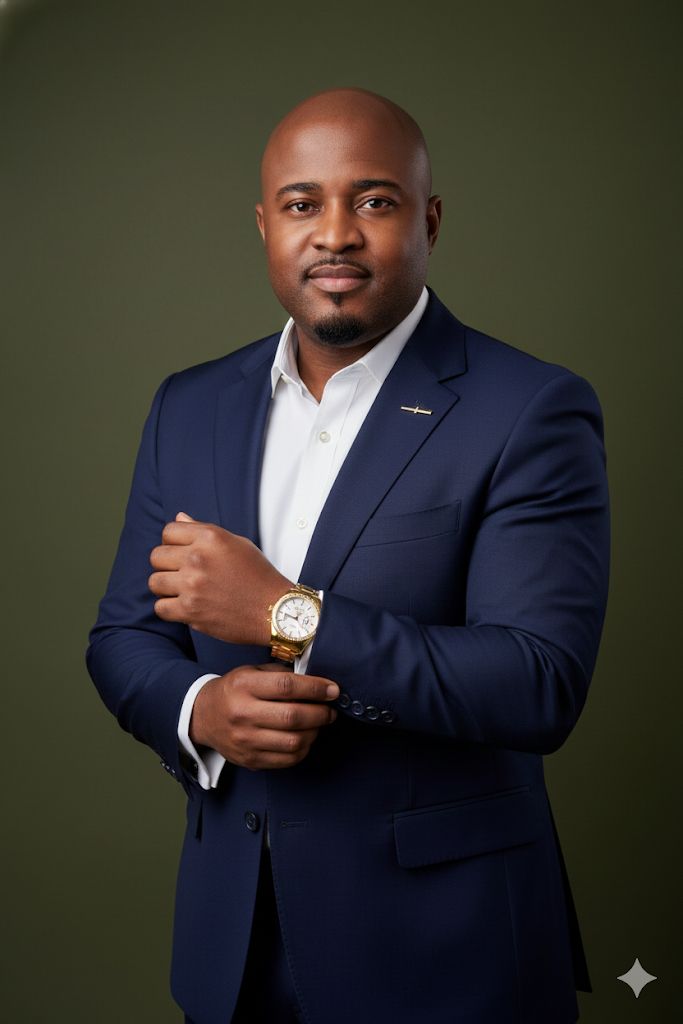
My approach connects technical depth with operational judgment—from the first alert through containment, remediation, and executive reporting.
Lead high-sensitivity investigations, coordinate escalation, and own the response lifecycle through closure.
Enrich indicators, connect attacker behavior to campaigns, and translate intelligence into proactive defenses.
Prioritize exposure through risk, threat context, and asset criticality—then validate remediation at scale.
Strengthen endpoint and network controls across complex enterprise and federal technology environments.
As threat actors increasingly use artificial intelligence to accelerate reconnaissance, social engineering, phishing, and other malicious activities, cybersecurity defenders must also use AI to strengthen their detection and response capabilities. AI can help analysts process large volumes of security data, correlate related activity, identify patterns, and investigate potential threats more efficiently.
However, AI should support—not replace—analytical judgment. I use Microsoft Security Copilot to accelerate investigations while independently validating its findings against the original security telemetry. Every determination remains evidence-based, whether an alert is ultimately classified as a true positive, false positive, or inconclusive.
These visual frameworks translate complex investigations into clear, repeatable workflows for analysts, defenders, and security leaders. Select either image to view it in full detail.
An evidence-driven, end-to-end model covering alert triage, evidence collection, threat hunting, determination, containment, reporting, and lessons learned.
View full mind map ↗A simulated investigation workflow demonstrating responsible AI-assisted triage, evidence validation, KQL generation, response decisions, and documentation.
View full mind map ↗I combine advanced research in cybersecurity leadership with industry certifications and day-to-day experience defending real systems.
For cybersecurity leadership, engineering, research, or collaboration opportunities, connect with me on LinkedIn.